Appendix B — Security-Approval (ATO) Kit
Boundary diagram, outbound endpoints, FedRAMP audit scope, Graph permission justification, token-folder mitigation, break-glass design and a licensing bill of materials
The authorization boundary, interconnection and leveraged-authorization language, and the risk decision belong to the agency’s authorizing official. This kit collects the facts an assessor will ask for. Platform facts were checked on 19 October 2026 and apply to Microsoft’s commercial cloud, including GCC-Moderate; see Applicability for GCC High and DoD.
Appendix_B-bundle.docx — this appendix as one Word document. Regenerated on every site deploy.
Boundary
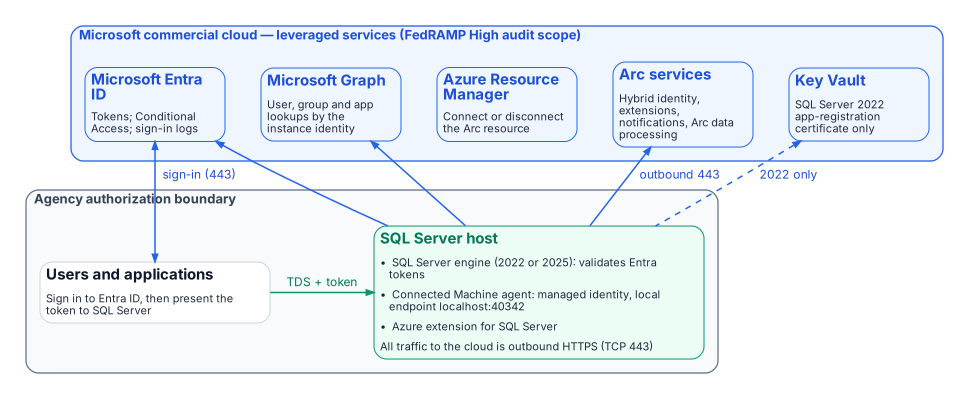
The SQL Server host stays inside the boundary. What changes is that it now depends on leveraged cloud services: Microsoft Entra ID for tokens, Microsoft Graph for lookups of users, groups and applications, and the Azure Arc services for the agent and the SQL extension. The Connected Machine agent communicates outbound to Azure Arc over TCP port 443.1 Azure Private Link can carry the Arc service traffic, but “network traffic to Microsoft Entra ID and Azure Resource Manager doesn’t traverse the Azure Arc private link scope and continues to use your default network route to the internet.”2
Outbound endpoints
From Microsoft’s network requirements for the Connected Machine agent (Azure public cloud) and the prerequisites for SQL Server enabled by Azure Arc:3 4
| Endpoint | Purpose | When required |
|---|---|---|
download.microsoft.com |
Windows installation package | Installation only |
login.microsoftonline.com |
Global Microsoft Entra token endpoint (onboarding and fallback) | Always |
*.login.microsoft.com |
Regional Microsoft Entra token endpoints | Always |
pas.windows.net |
Microsoft Entra ID | Always |
management.azure.com |
Azure Resource Manager: create or delete the Arc server resource | Connect or disconnect only |
*.his.arc.azure.com |
Metadata and hybrid identity services | Always |
*.guestconfiguration.azure.com |
Extension management and guest configuration | Always |
guestnotificationservice.azure.com, *.guestnotificationservice.azure.com |
Notification service | Always |
azgn*.servicebus.windows.net or *.servicebus.windows.net |
Notification service | Always |
*.<region>.arcdataservices.com |
Arc data processing service for Arc-enabled SQL Server | If Arc-enabled SQL Server is used |
<key-vault-name>.vault.azure.net, graph.microsoft.com |
Microsoft Entra authentication with Arc-enabled SQL Server | If Arc-enabled SQL Server is used |
Use Microsoft’s page, not this table, as the firewall source of truth: it lists optional endpoints (Windows Admin Center, SSH, ESU certificates, license validation) and changes over time.
FedRAMP audit scope of each leveraged service
Microsoft’s compliance-scope page lists each of these Azure public-cloud services as in scope for FedRAMP High (page dated 21 September 2026):5
| Service | Role in this design | FedRAMP High (Azure public) |
|---|---|---|
| Microsoft Entra ID (P1 + P2) and Microsoft Entra multifactor authentication | Tokens, Conditional Access, MFA, sign-in logs | ✅ |
| Microsoft Entra ID Governance | PIM for Groups, access reviews (Book 07) | ✅ |
| Microsoft Graph | Instance-identity lookups | ✅ |
| Azure Arc-enabled servers | Connected Machine agent, managed identity | ✅ |
| Azure Arc-enabled SQL Server | Azure extension for SQL Server | ✅ |
| Azure Resource Manager | Arc resources | ✅ |
| Key Vault | SQL Server 2022 certificate | ✅ |
| Azure Monitor (incl. Log Analytics) | Telemetry (Book 09) | ✅ |
| Microsoft Defender for Cloud | Defender for SQL (Book 09) | ✅ |
| Microsoft Intune | Cloud PKI (Book 10) | ✅ |
An audit-scope listing is not the agency’s authorization. Leveraging a provider authorization still needs the agency’s own review of the package and of customer responsibilities.
Graph permissions for each machine identity
What is required. “Each system-assigned managed identity requires User.Read.All, GroupMember.Read.All, and Application.Read.All permissions to query Microsoft Graph.” They are application permissions (app roles) that “must be assigned directly to each managed identity” and “can’t be manually assigned to a Microsoft Entra security group.” Only a Privileged Role Administrator or higher can grant them.6 The SQL Server 2022 app-registration setup documents either Directory.Read.All or the narrower set Application.Read.All, Group.Read.All and User.Read.All; choose the narrower set.7
Least-privilege justification.
User.Read.Allresolves the Entra users thatCREATE LOGIN … FROM EXTERNAL PROVIDERnames and that connect.GroupMember.Read.Allresolves group membership for type-X (group) logins, which is how Book 07 grants access.Application.Read.Allresolves service principals and managed identities that connect as applications (Book 08).- All three are read-only. None grants write access to the directory.
Why not Directory Readers. Microsoft offers assigning the Directory Readers role to a role-assignable group as an alternative for many machines, but notes that it “grants broad read access across all directory objects, significantly exceeding the three targeted Graph API permissions,” and that it “isn’t recommended for production environments where least-privilege access is required.”8 Grant the three app roles to each identity with a script, and review the grants with the rest of the access reviews.
Token folder and BULK permissions
Microsoft documents that “OPENROWSET BULK operations can also read the tokens folder C:\ProgramData\AzureConnectedMachineAgent\Tokens\,” and that the ADMINISTER BULK OPERATIONS and ADMINISTER DATABASE BULK OPERATIONS permissions “should be treated as equivalent to sysadmin.”9 The mitigation:
- Grant either permission only to principals that already hold
sysadmin, and record any exception in the exception registry. - Include both permissions in the audit’s privileged-permission report and in SQL Server Audit, alongside
sysadminmembership. - The agent’s local identity endpoint requires the caller to be in the local Administrators group or the Hybrid Agent Extension Applications group,10 so manage those memberships as privileged.
Break-glass design
| Failure | Design |
|---|---|
| Entra ID or Graph unreachable | Entra logins can’t authenticate. Keep one documented break-glass path: a Windows group holding sysadmin, empty by default, in the exception registry, with every membership change and every login alerting. |
Every sysadmin path lost |
Microsoft documents starting the instance in single-user mode; a member of the computer’s local Administrators group can then connect as sysadmin.11 That is why local Administrators membership on SQL hosts is itself privileged. |
| Tenant-side lockout | Follow Microsoft’s emergency-access account guidance for the Entra tenant.12 |
| Pressure to turn Entra authentication off | Microsoft states that once Entra authentication is enabled with a managed identity, disabling it isn’t advisable, and forcibly deleting registry entries can cause unpredictable behavior.13 Recover through the paths above instead. |
Licensing bill of materials
List prices change and agreements differ, so this table names the license each capability needs, not its price.
| Book | Capability | License | Source |
|---|---|---|---|
| 02–03 | Arc inventory and the audit | SQL Server license; Arc’s client connection summary needs Software Assurance, a SQL Server subscription or pay-as-you-go | 14 |
| 04–05 | Entra authentication on the engine | Available with “License only” — no Software Assurance or pay-as-you-go needed | 15 |
| 04 | SQL Server 2022 certificate | Azure Key Vault (consumption) | 16 |
| 05, 07, 09 | Conditional Access (MFA, device, location, risk) | Microsoft Entra ID P1 | 17 |
| 07 | Dynamic membership groups | Microsoft Entra ID P1 for each unique member | 18 |
| 07 | PIM for Groups | Microsoft Entra ID P2, ID Governance or Entra Suite | 19 |
| 07 | Access reviews | Microsoft Entra ID Governance or Entra Suite | 20 |
| 09 | Defender for SQL servers on machines | A Microsoft Defender for Cloud plan | 21 |
| 09 | Log Analytics | Azure Monitor (consumption) | — |
| 10 | Microsoft Cloud PKI | Intune add-on, standalone or in the Intune Suite | 22 |
Footnotes
Microsoft Learn, Connected Machine agent network requirements. Checked 19 October 2026.↩︎
Microsoft Learn, Use Azure Private Link to connect servers to Azure Arc by using a private endpoint.↩︎
Microsoft Learn, Connected Machine agent network requirements. Checked 19 October 2026.↩︎
Microsoft Learn, Prerequisites — SQL Server enabled by Azure Arc.↩︎
Microsoft Learn, Azure and other Microsoft cloud services compliance scope, “Azure public services by audit scope”. Checked 19 October 2026.↩︎
Microsoft Learn, Set up managed identity and Microsoft Entra authentication for SQL Server enabled by Azure Arc, “Grant application permissions to the identity”.↩︎
Microsoft Learn, Set up Microsoft Entra authentication with app registration — SQL Server enabled by Azure Arc.↩︎
Microsoft Learn, Set up managed identity and Microsoft Entra authentication for SQL Server enabled by Azure Arc, “Grant application permissions to the identity”.↩︎
Microsoft Learn, Managed identity overview — SQL Server enabled by Azure Arc, Limitations.↩︎
Microsoft Learn, Access Azure resources with managed identity on Azure Arc-enabled servers.↩︎
Microsoft Learn, Connect to SQL Server when system administrators are locked out.↩︎
Microsoft Learn, Manage emergency access admin accounts.↩︎
Microsoft Learn, Managed identity overview — SQL Server enabled by Azure Arc, Limitations.↩︎
Microsoft Learn, Overview — SQL Server enabled by Azure Arc, feature availability by license type.↩︎
Microsoft Learn, Overview — SQL Server enabled by Azure Arc, feature availability by license type.↩︎
Microsoft Learn, Set up Microsoft Entra authentication with app registration — SQL Server enabled by Azure Arc.↩︎
Microsoft Learn, What is Conditional Access?, License requirements.↩︎
Microsoft Learn, Manage rules for dynamic membership groups in Microsoft Entra ID, License requirements.↩︎
Microsoft Learn, Microsoft Entra ID Governance licensing fundamentals.↩︎
Microsoft Learn, What are access reviews?, License requirements.↩︎
Microsoft Learn, Microsoft Defender for SQL servers on machines overview.↩︎
Microsoft Learn, Microsoft Cloud PKI for Microsoft Intune.↩︎