Book_03 — Discovery: The Authentication Audit
The Authentication-Audit Script, the Arc-Eligibility Classification, and the Compliance-Monitoring Telemetry Sink
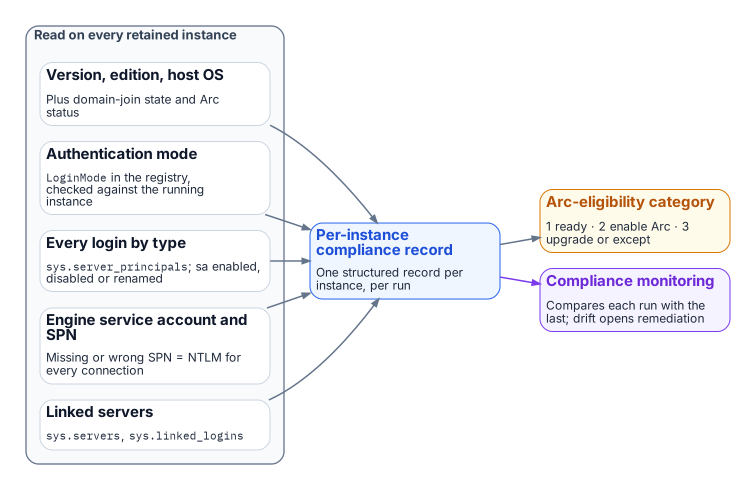
No migration survives contact with an estate it has not measured. Describes the authentication-audit script discovery instrument — what it captures (instances, authentication mode, login types, service accounts, SPN registration), the three-category Arc-eligibility classification that drives migration sequencing, and how its output feeds the compliance-monitoring pipeline as a living compliance record rather than a point-in-time spreadsheet.
Note
Where Book 02 measured the estate to decide what survives, this book measures the authentication posture of what remains. The authentication-audit script is the instrument, the Arc-eligibility classification is its most consequential output, and the per-instance compliance record — not a spreadsheet — is its deliverable.
TipDownload this book
Book_03-bundle.docx — every chapter of this book concatenated into one Word document. Regenerated on every site deploy.
Chapters
| Title |
|---|
| The Authentication-Audit Script: What It Measures and Why |
| Reading the Audit: Classification and Triage |
No matching items
Place in the dependency chain: Step 3 — Audit survivors.