Book_05 — The Login Migration: Windows Principals to Entra Logins
The Technical Heart of the Series — FROM EXTERNAL PROVIDER and the Parallel-Run Cutover
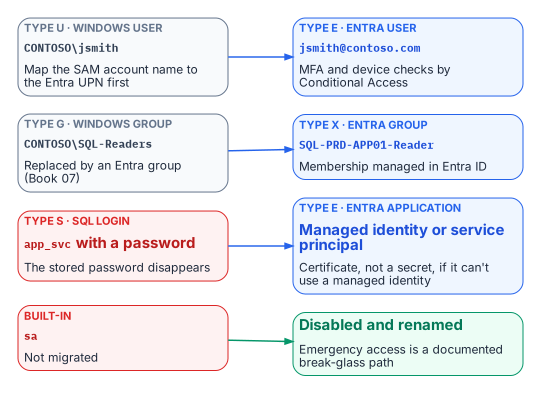
The moment the SQL Server engine stops accepting Kerberos tickets and Windows challenge-response and starts accepting Entra ID-issued OAuth 2.0 tokens. Describes the three principal types (Entra user, Entra security group, Entra service principal), the FROM EXTERNAL PROVIDER syntax that makes the migration possible on SQL Server 2022, the three-phase parallel-run cutover pattern, and the engineering decisions the SQL Server engine-authentication decision formalizes.
Note
Everything in Books 01 through 04 is prerequisite; everything in Books 06 through 09 is consequence. This book is the migration itself — performed only on the instances Book 02 classified retain or target, using the three-phase parallel-run pattern that the SQL Server engine-authentication decision makes normative.
TipDownload this book
Book_05-bundle.docx — every chapter of this book concatenated into one Word document. Regenerated on every site deploy.
Chapters
| Title |
|---|
| Three Principal Types — User, Group, Service Principal |
| What the Engine-Authentication Decision Settles |
No matching items
Place in the dependency chain: Steps 5 and 7 — Introduce Entra principals, then remove legacy principals.