Book_04 — Arc as the Identity Bridge
How the Azure Connected Machine Agent Gives the SQL Server Engine a Cloud-Native Identity
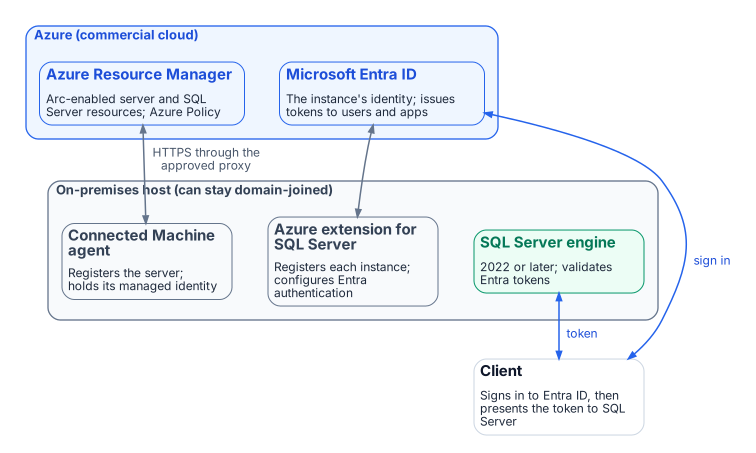
Without Arc, the SQL Server engine has no cloud-native identity; without that identity, there is nothing to anchor the instance’s Entra identity — the managed identity on SQL Server 2025, or the app registration certificate the Arc agent installs on SQL Server 2022 — and no mechanism to accept Entra ID-issued tokens.123 This book explains exactly what Arc does and does not change — and why SQL engine Entra auth (Layer 1) must not be blocked on the domain unjoin that OS-level Entra login (Layer 2) requires.
Book_04-bundle.docx — every chapter of this book concatenated into one Word document. Regenerated on every site deploy.
Chapters
| Title |
|---|
| What Arc Provides to SQL Server |
| Arc Deployment Sequencing for SQL Server Hosts |
Place in the dependency chain: Step 4 — Enable identity substrate.
Footnotes
Microsoft Learn, Microsoft Entra authentication for SQL Server overview.↩︎
Microsoft Learn, Managed identity overview — SQL Server enabled by Azure Arc.↩︎
Microsoft Learn, Set up Microsoft Entra authentication with app registration — SQL Server enabled by Azure Arc.↩︎