Book_08 — The Application Chain: LDAP-Bound and SQL-Consuming Applications
Following the Transformation Upstream Into the Middleware Layer
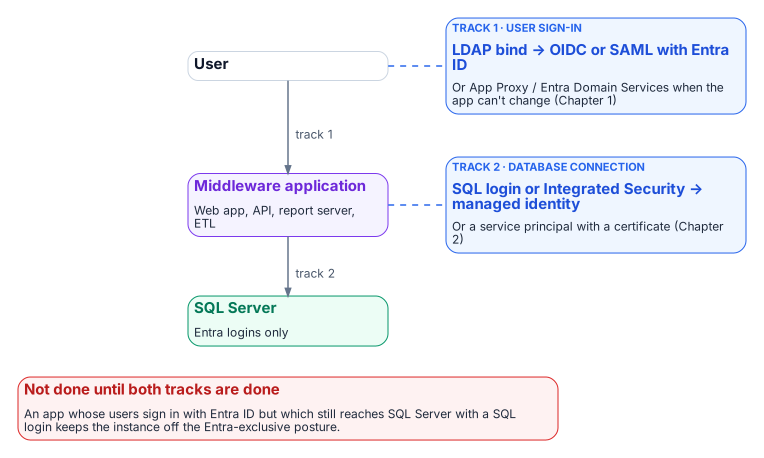
SQL Server does not exist in isolation — it is downstream of applications, many of them LDAP-bound. Applies the LDAP-dependent-application migration plan’s four-class migration taxonomy (App Proxy, SAML, OIDC, Entra Domain Services) specifically to SQL-consuming applications, traces the authentication chain from the user’s Entra credential through the application to the SQL connection, and describes the connection-string migration as the last mile.
Note
An upstream application that has migrated its user authentication to Entra ID but still uses a SQL Authentication service account to reach the database has not completed its transformation. The application chain must be addressed as a complete authentication path, not as independent layers.
TipDownload this book
Book_08-bundle.docx — every chapter of this book concatenated into one Word document. Regenerated on every site deploy.
Chapters
| Title |
|---|
| The Four-Class Pattern Applied to SQL-Consuming Applications |
| Connection String Migration: The Last Mile |
No matching items
Place in the dependency chain: Step 6 — Move applications.