Book_07 — Access Control: Groups, Roles, and Dynamic Membership
Designing the Entra Groups Behind SQL Server Access — Role-Mapped Groups, Attribute-Driven Membership, Scoped Delegation, and Just-in-Time Privilege
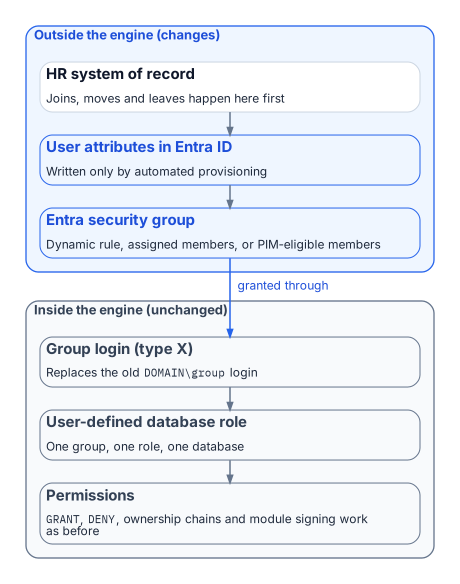
The migration moves SQL Server’s groups from Active Directory to Microsoft Entra ID, but it keeps group-based authorization. What changes is who maintains the groups and how. A group that maps to a single database role can keep itself current from HR-sourced attributes, which removes the helpdesk ticket. That only works if the attributes are trustworthy, the rules are tested, delegation is scoped, and privileged access is just-in-time. This book covers that design and the governance it needs.
Book_07-bundle.docx — every chapter of this book concatenated into one Word document. Regenerated on every site deploy.
Chapters
| Title |
|---|
| Groups, Roles, and How Membership Reaches the Engine |
| Dynamic Membership, Delegation, and Privileged Access |
Place in the dependency chain: Step 5 — Introduce Entra principals (groups and authorization).