Book_10 — Certificate Authority: From ADCS to Microsoft Cloud PKI
The Infrastructure Dependency Most SQL Server Transformation Documents Ignore
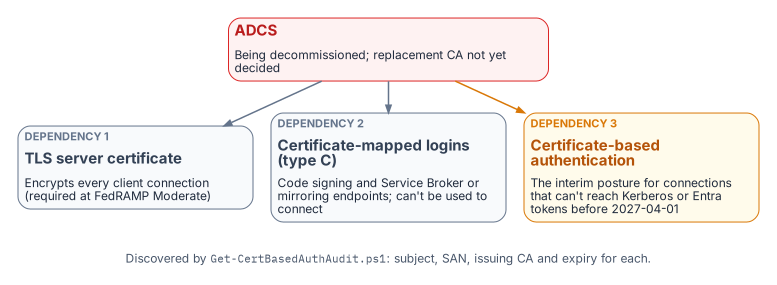
The transformation inventory classifies the ADCS-to-Microsoft Cloud PKI transformation as ‘Not Yet Defined.’ Documents why the SQL Server narrative cannot be complete without addressing certificate infrastructure: three distinct SQL Server capabilities — TLS encryption, certificate-mapped logins, and Certificate-Based Authentication as the Kerberos/NTLM-elimination program’s NTLM-replacement interim posture — depend on ADCS-issued certificates. Analytical and motivational; cites no normative architecture decision because none has been authored.
Warning
This book documents a “Not Yet Defined” gap from the transformation inventory. The content is analytical and motivational — it identifies the dependencies, names the gap, and describes what the as-yet-unwritten ADCS-migration architecture decision must address. Get-CertBasedAuthAudit.ps1 is the discovery instrument. Do not cite this book as normative governance for ADCS-migration decisions.
TipDownload this book
Book_10-bundle.docx — every chapter of this book concatenated into one Word document. Regenerated on every site deploy.
Chapters
| Title |
|---|
| Where SQL Server Touches ADCS |
No matching items
Place in the dependency chain: The certificate dependency behind steps 4 and 8.